Cybersecurity researchers from LastPass and Delphos Labs have uncovered a complex, multi-layered malware campaign that leverages search engine optimization (SEO) poisoning on GitHub to impersonate dozens of high-profile software brands. The campaign’s primary objective is the distribution of a previously undocumented information-stealing trojan designated as "Rapuncel," alongside a Microsoft-signed kernel driver capable of systematically disabling 145 distinct endpoint detection and response (EDR) and antivirus solutions.
This coordinated threat highlights a persistent and evolving trend in cybercriminal methodology: the weaponization of trusted developer platforms and legitimate code-signing certificates to establish deep persistence and evade modern enterprise defenses. By manipulating search results, threat actors are able to redirect unsuspecting users searching for everyday productivity and security utilities—such as the LastPass Authenticator—straight into malicious download funnels.
The Attack Chain: From Search Bar to System Compromise
The sophisticated intrusion lifecycle begins well before a victim ever interacts with a malicious repository. Threat actors utilize SEO optimization techniques to push fraudulent GitHub repositories to the top of search engine results when users look for popular utilities, software development tools, or brand-name applications. The campaign has been found to impersonate at least 40 prominent software companies and brands, creating a veneer of legitimacy that lowers the guard of even technically proficient users.
Once a target locates one of these deceptive GitHub pages and clicks the download link, they are not immediately served a file. Instead, the action triggers a rapid series of HTTP redirections designed to obfuscate the origin of the traffic and route the browser to payload-delivery infrastructure. At the end of this redirection chain, the victim receives a compressed ZIP archive.
To bypass automated security scans and cloud-based file-size inspection thresholds, the attackers artificially bloat the ZIP archives to sizes reaching up to 148 megabytes. Within these bulky archives sits an installer file that appears innocuous at first glance. The installer is actually a legitimate copy of the Microsoft Visual Studio CoreCLR Debugger, known as vsdbg.exe, which has been renamed and tactically configured to perform DLL sideloading. When executed, the legitimate binary loads a malicious companion file named vsdbg.dll.
This sideloading mechanism acts as the catalyst for a dual-pronged payload deployment. It simultaneously installs the Rapuncel infostealer to harvest sensitive data and drops a malicious kernel driver designated as Alinubx.sys.
Weaponized Kernel-Level EDR Killer
Perhaps the most alarming technical aspect of the campaign is the deployment of the Alinubx.sys kernel driver. Disguised as an NVIDIA component named nvfsflt64.sys and registered under the system service name NvFsFilter, the driver functions as an aggressive EDR killer designed to neutralize security software before the data-theft phase begins.
According to technical analyses published by LastPass and Delphos Labs, the driver contains a hardcoded target list of 145 different antivirus and endpoint protection processes. To bypass standard operating system security controls, the driver leverages low-level kernel APIs.
"The driver calls ObOpenObjectByPointer with AccessMode=KernelMode, which bypasses the normal user-mode SeAccessCheck path at handle-open time," LastPass detailed in its technical advisory. "It asks the kernel to open the process as kernel code, then kills it. That is why it can defeat Protected Process Light (PPL); the protection many security products rely on to survive an administrator."
Compounding the severity of this threat is the pedigree of the driver itself. The Alinubx.sys file is cryptographically signed through Microsoft’s legitimate Windows Hardware Compatibility Publisher certificate chain, allowing it to load successfully on modern versions of Windows without triggering driver-signing enforcement warnings. Furthermore, at the time of discovery, the driver had not yet been added to Microsoft’s official vulnerable and malicious driver blocklist (known as the Driver Blocklist).
Security researchers noted that while the driver includes advanced capabilities for file and registry hiding, dynamic link library (DLL) injection, process interception, traffic manipulation, and port redirection, these additional features appear to remain dormant in the current iteration of the campaign, indicating a focused and modular approach by the threat actors.
Inside the Rapuncel Infostealer
With the host system’s protective mechanisms forcibly terminated by the kernel driver, the Rapuncel infostealer initiates its data-harvesting routines. Security assessments indicate with moderate confidence that Rapuncel operates as a distinct variant of the known BoryptGrab family, while its underlying loader was constructed utilizing the Cruciferra PUROSANGUE crypter.
Rapuncel is engineered to systematically vacuum valuable data from the compromised environment. The malware targets browser credentials, session cookies, cryptocurrency wallets, local configuration files, and system identification metadata.
To overcome modern browser security measures—specifically Google’s app-bound encryption implemented in Chromium-based browsers like Google Chrome and Microsoft Edge—Rapuncel employs an advanced evasion technique. The malware injects a custom helper DLL directly into the browser application and invokes its own proprietary Elevation Service to decrypt and extract sensitive data that would otherwise remain shielded from user-space applications.
Once compiled and structured, the stolen information is compressed into an archive and exfiltrated to an external command-and-control (C2) endpoint located at 2.26.126[.]50. The transmission is executed via raw TCP using HTTP-formatted data requests, minimizing the footprint left on standard application-layer logging tools.
To ensure long-term viability within the enterprise or consumer network, Rapuncel establishes system persistence across reboots by registering itself as a native Windows service. This configuration ensures that even if a terminated security product manages to restart or recover following a system event, the Rapuncel service instantly reacts, re-engaging the kernel driver to kill the security software anew before executing its secondary loops.
Background Context and Chronological Evolution
The discovery of the Rapuncel campaign underscores a broader, long-term shift in cybercrime toward exploiting the software supply chain and developer trust networks. Over the past several years, threat actors have increasingly targeted platforms like GitHub, npm, PyPI, and Docker Hub not only to distribute malicious code to developers but also to trick everyday consumers who turn to code-sharing repositories for freeware utilities, patches, and alternative software downloads.
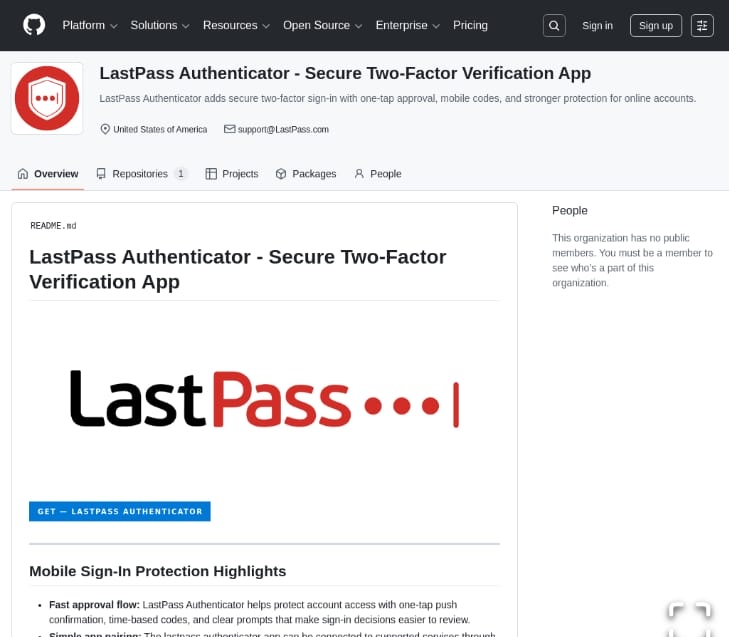
SEO poisoning—the practice of manipulating search engine algorithms through black-hat optimization techniques to rank malicious links above legitimate ones—has become a preferred vector for initial access. By capitalizing on brand recognition, attackers bypass the friction associated with traditional phishing emails, targeting victims at the exact moment of intent when they are actively seeking to install specific software.
The use of Bring Your Own Vulnerable Driver (BYOVD) and abused legitimate code-signing certificates to bypass Endpoint Detection and Response solutions represents an escalating arms race in cybersecurity. While operating system vendors and security firms continuously tighten driver-signing requirements and expand blocklists, threat actors consistently find ways to acquire or abuse valid signing certificates to inject malicious code directly into the Windows kernel.
Industry Implications and Broader Impact
The implications of this campaign extend far beyond individual consumer infections, posing notable risks to corporate environments where employees frequently utilize personal devices or unvetted developer tools.
When enterprise endpoints are compromised by a dual-threat mechanism comprising an advanced infostealer and a kernel-level EDR killer, organizations face immediate risks of credential theft, corporate espionage, and lateral network movement. The ability of malware to blindly terminate 145 distinct security products demonstrates a high level of research and development capability by the threat actors, signaling that modern malware is increasingly built with environmental resilience in mind.
Furthermore, the abuse of Microsoft’s code-signing infrastructure highlights systemic challenges in certificate authority validation and hardware developer program oversight. When malicious drivers can be signed with legitimate publishing chains and evade immediate blocklisting, the foundational trust placed in cryptographic signatures is momentarily undermined, requiring security teams to rely heavily on behavioral analysis rather than simple static indicators of compromise.
Mitigation and Defensive Recommendations
In response to the Rapuncel campaign, cybersecurity analysts, software vendors, and threat intelligence organizations have issued critical guidance for both individual users and enterprise system administrators.
- Source Verification: Users are strongly advised to download software exclusively from official, verified vendor websites. Third-party repositories, unofficial mirrors, and unfamiliar GitHub projects should be treated with extreme caution, particularly when encountered via sponsored or promoted search engine results.
- Search Engine Vigilance: Organizations should educate employees on the risks associated with SEO poisoning and recommend the use of ad-blocking extensions or direct navigation to known vendor URLs rather than relying on top search engine results for software downloads.
- Driver Blocklist Enforcement: Enterprise security teams should ensure that their endpoint protection platforms and operating systems are configured to utilize and frequently update Microsoft’s recommended vulnerable driver blocklists, mitigating the risk of BYOVD attacks.
- Behavioral Monitoring: Given the ability of advanced infostealers to bypass static file checks and user-space security controls, organizations must prioritize behavioral monitoring, network traffic analysis, and anomaly detection to identify unauthorized kernel-level interactions and raw TCP exfiltration attempts.
As threat actors continue to refine their evasion techniques, combining SEO manipulation with kernel-level defenses, the discovery of the Rapuncel campaign serves as a timely reminder of the vigilance required to secure modern digital ecosystems against sophisticated, multi-vector intrusions.