New Brazilian Banking Malware Campaign Kremlin Leverages Blockchain Infrastructure to Evade Detection

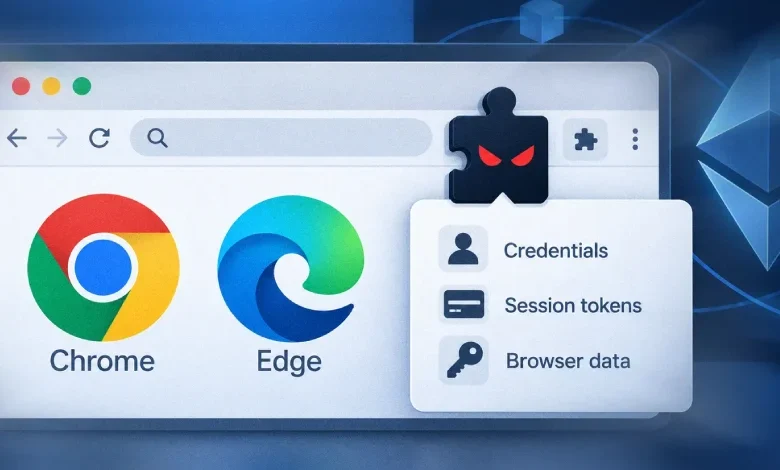
Cybersecurity researchers have uncovered a sophisticated and highly resilient banking malware operation targeting financial institutions across Brazil. Identified by Elastic Security Labs as the REF9334 threat actor, this campaign centers on the deployment of a specialized toolkit dubbed KREMLIN. Since its inception in May 2025, the group has demonstrated a remarkable ability to evolve, transitioning from standard trojan distribution to a complex, multi-stage architecture that utilizes blockchain technology to mask its command-and-control (C2) infrastructure.
The Anatomy of the KREMLIN Operation
The KREMLIN malware ecosystem is characterized by its modular design, utilizing a sophisticated chain of JavaScript loaders and custom C++ installers. The primary objective of the campaign is the silent deployment of malicious browser extensions on Google Chrome and Microsoft Edge, which are subsequently used to harvest sensitive credentials, session tokens, and financial data from unsuspecting users.
The attack vector typically begins with a social engineering lure. Users are tricked into executing a seemingly benign file, often disguised as a legitimate banking document, an invoice, or a corporate memo. Once the initial JavaScript file is executed, the malware initiates a series of rigorous environmental checks. These checks are designed to detect if the code is being run within a sandbox or a virtual machine—common environments used by security researchers to analyze malware behavior. If the malware detects these defensive environments, it immediately terminates to prevent analysis.

Chronology and Operational Evolution
The timeline of the REF9334 activity suggests a group that is constantly iterating its tactics. While the group has been active since at least May 2025, distributing well-known malware such as Pulsar RAT and Remcos RAT, the introduction of the KREMLIN toolkit represents a significant shift in operational maturity.
- May 2025: Initial signs of the threat actor emerge, focusing on the distribution of off-the-shelf remote access trojans (RATs).
- June 16, 2025: The first of seven distinct campaigns attributed to this specific group begins.
- May 19, 2026: A critical pivot occurs as the group integrates Ethereum smart contracts into their infrastructure. This move effectively decentralized their command-and-control points, making it significantly harder for security researchers to disrupt the operation by blocking a single server or domain.
- August 2026: Parallel observations of similar browser-based exploitation techniques by other actors, such as the China-linked APT31, suggest a broader industry trend toward abusing browser integrity mechanisms to maintain persistence.
Blockchain-Based Evasion Techniques
Perhaps the most innovative aspect of the KREMLIN operation is the use of the Ethereum blockchain as a "dead drop resolver." By embedding specific smart contracts into their code, the attackers can dynamically update their C2 server addresses and payload hosting locations in real-time. Because these updates occur on a public, immutable ledger, security vendors cannot easily "sinkhole" the traffic or seize the infrastructure. This creates a resilient, self-updating loop that keeps the malware active even if individual nodes are taken offline.
Furthermore, the malware employs a "network canary" mechanism. Before proceeding with its primary functions, the payload attempts to connect to an unregistered domain. If the connection succeeds, it indicates that the system is likely being monitored by security software attempting to simulate a network connection. In such an event, the malware forces a crash to avoid detection. Elastic Security Labs reported that they successfully registered one of these canary domains, providing them with a window into the scale of the campaign. Data from these pings suggests that over 1,515 systems have been compromised, with more than 98% of these victims located in Brazil.
Bypassing Chromium Integrity Mechanisms
The malicious browser extensions installed by KREMLIN—most notably the one masquerading as "AVSync System Inc."—are designed to operate with deep-level access. To install these extensions without alerting the user or triggering browser security warnings, the attackers leverage advanced techniques known as "Phantom Extension" and "GhostChrome-X."

These methods allow the malware to modify the browser’s "Secure Preferences" file. Under normal circumstances, modifying this file would invalidate the browser’s internal security checks, causing the extension to be disabled. The KREMLIN malware bypasses this by recalculating the required Hash-based Message Authentication Codes (HMACs) and App-Bound encrypted hashes, effectively tricking the browser into believing the extension is legitimate and verified.
Once the extension is successfully installed, it requests broad permissions, including access to all browser tabs, cookies, storage, and the webRequest API. This allows the threat actor to monitor web traffic in real-time, intercept login credentials, and exfiltrate session cookies, enabling them to bypass multi-factor authentication (MFA) in many instances.
Broader Implications and Defensive Challenges
The KREMLIN operation highlights a growing trend in cyber-espionage and financial fraud: the shift from host-based malware to browser-based exploitation. By focusing on the browser, attackers can bypass traditional antivirus solutions that primarily monitor file systems and memory. Because modern users conduct the vast majority of their financial and professional activities within the browser, this "man-in-the-browser" approach is highly effective.
"Malicious browser extensions bypass Chromium integrity mechanisms by manipulating Secure Preferences and regenerating required HMACs and App-Bound encrypted hashes," noted security researchers Cyril François and Andrew Pease of Elastic Security Labs. Their findings underscore the difficulty of securing modern endpoints when attackers are willing to abuse the very mechanisms designed to protect the integrity of the browser environment.

The use of decentralized infrastructure also poses a significant challenge for law enforcement and threat intelligence organizations. Traditional takedown efforts rely on the cooperation of domain registrars, hosting providers, and cloud service providers. When an attacker shifts their command infrastructure to a blockchain-based resolver, there is no centralized entity to contact to disable the malicious traffic.
Strategic Recommendations for Organizations
Defenders are urged to monitor for indicators of compromise (IoCs) associated with the KREMLIN campaign. Specifically, security teams should look for:
- Unexpected browser modifications: Regularly audit the "Secure Preferences" files and installed extensions across organizational endpoints, specifically looking for extensions with broad, unnecessary permissions.
- Unusual process behavior: Monitor for instances where legitimate binaries (like those from SentinelOne or other security tools) are being used for binary sideloading.
- Network anomalies: While the C2 infrastructure is decentralized via blockchain, the communication between the browser extension and the C2 servers (such as
luizestrelhashapr[.]online) can be detected at the network perimeter. - Endpoint hardening: Enforce strict group policies that prevent the installation of extensions not authorized by the organization and restrict the use of developer mode in Chromium-based browsers.
As the REF9334 actor continues to refine their toolkit, the security community must adapt by moving beyond signature-based detection. Behavioral analysis, particularly focusing on the integrity of browser configuration files, will be essential in identifying and neutralizing these types of threats before they can exfiltrate sensitive financial data. The KREMLIN campaign serves as a sobering reminder that the intersection of blockchain, sophisticated social engineering, and browser-level manipulation creates a new frontier of threat that requires heightened vigilance from both enterprises and individual users alike.