Check Point Security Alert: Critical Vulnerabilities Under Active Exploitation Impact Management Servers and VPN Gateways

Check Point Software Technologies has issued urgent security advisories regarding two high-severity vulnerabilities currently being exploited in the wild, prompting a widespread call for immediate patching across its enterprise and small-business product lines. The security giant confirmed that a previously unknown flaw in its Security Management Server, designated CVE-2026-93616, was leveraged in targeted attacks as early as July 23, 2026. Simultaneously, the company is managing the fallout from a separate, critical VPN-related vulnerability, CVE-2026-85102, which has been subject to active exploitation attempts against Spark firewall customers since September 12, 2026.
These developments represent a significant challenge for network administrators, as both vulnerabilities pose severe risks to infrastructure integrity. CVE-2026-93616, which carries a near-perfect CVSS score of 9.8, allows unauthorized remote code execution, while the VPN flaw threatens the secure perimeter of small-to-medium enterprise (SME) environments.
Anatomy of the Management Server Breach (CVE-2026-93616)
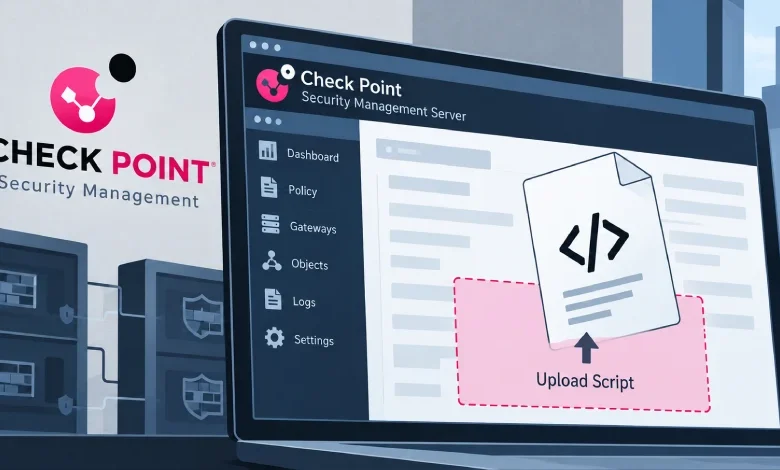
The most alarming development involves CVE-2026-93616, a path traversal vulnerability residing within the Security Management Server’s web service. By failing to properly sanitize user input, the service allows an unauthenticated attacker to manipulate file paths, ultimately enabling the upload and execution of malicious scripts directly on the server.
Because the Security Management Server serves as the central control plane for entire firewall estates, a compromise here is catastrophic. An attacker with control over this server can push malicious security policies to every gateway under its management, effectively granting them control over the organization’s entire network traffic flow.
The July 23 incident highlights the sophistication of the threat actors involved. While Check Point has remained tight-lipped regarding the specific identity of the targets, the nature of the exploit—which requires precise knowledge of the server’s web architecture—suggests a high level of research and preparation. The lack of public disclosure regarding the aftermath of these attacks leaves industry analysts to speculate on the potential for data exfiltration, lateral movement, or the long-term planting of backdoors within corporate networks.

Chronology of Exploitation and Remediation
The timeline of these vulnerabilities reveals a difficult landscape for security teams attempting to maintain compliance and defense.
- July 23, 2026: Initial exploitation of the undisclosed CVE-2026-93616 flaw observed in the wild.
- September 9, 2026: Check Point releases initial patches for CVE-2026-85102 (VPN certificate flaw), believing at the time that no exploitation was occurring.
- September 12, 2026: Attackers begin active exploitation campaigns against the VPN flaw (CVE-2026-85102), specifically targeting Spark firewall users.
- September 16, 2026: A separate management server flaw (CVE-2026-91843) is addressed via LivePatch, though this update does not remediate the primary path traversal issue.
- September 22, 2026: Check Point officially acknowledges the existence of CVE-2026-93616 and issues the necessary security updates to close the vulnerability.
The delay between the initial July attacks and the September patch release has drawn scrutiny from the cybersecurity community. While "zero-day" vulnerabilities are notoriously difficult to identify, the three-month window of exposure for some high-profile clients emphasizes the need for more robust anomaly detection at the management layer.
The Spark Firewall and VPN Crisis (CVE-2026-85102)
While the management server issue affects larger enterprise deployments, the VPN flaw (CVE-2026-85102) poses an existential threat to smaller organizations utilizing Check Point’s Spark line. This vulnerability is rooted in the gateway’s certificate validation process during the establishment of a VPN tunnel.
If a gateway is not properly patched, an unauthenticated attacker can present a malicious certificate to the VPN service, bypassing standard authentication protocols to execute code on the device. The Netherlands’ National Cyber Security Centre (NCSC) has provided technical guidance, noting that the vulnerability is specifically triggered during Site-to-Site and Remote Access VPN negotiations.
Check Point’s telemetry indicates that the attackers are utilizing anonymizing infrastructure, including residential proxies and established VPN services, to mask their origins. The attackers are deploying certificates with specific identifiers, although security researchers warn that this is likely a fluid list designed to evade static signature-based detection.
Impact Analysis: The Threat to Centralized Control
The technical implications of these vulnerabilities are profound. In modern enterprise architecture, the centralization of security management—while efficient—creates a "single point of failure." By targeting the management server, attackers can bypass traditional perimeter defenses. If a threat actor controls the management interface, they can disable logging, whitelist their own IP addresses, or create "ghost" firewall rules that allow traffic to bypass inspection entirely without alerting local administrators.

Furthermore, the targeting of the Spark line, which is frequently used by smaller businesses with limited dedicated IT staff, suggests that threat actors are intentionally choosing "low-hanging fruit." Smaller organizations are statistically less likely to have comprehensive incident response plans or the resources to apply urgent "hotfixes" within a 24-hour window, making them ideal targets for mass-exploitation campaigns.
Official Guidance and Mitigation Strategies
For organizations operating Check Point infrastructure, the priority must be an immediate audit of version numbers and the application of patches identified in support articles sk1000171 and sk1000117.
Recommended Actions for Administrators:
- Version Verification: Immediately cross-reference current firmware and software versions against the affected lists published in the latest security advisories.
- Log Analysis: Audit VPN logs for unusual certificate-based Mobile Access logins. Specifically, search for activity post-login that involves internal network scanning or unexpected port enumeration.
- Network Hardening: For gateways that cannot be immediately patched, implement the NCSC-recommended workaround: disable implied VPN rules and restrict access to UDP ports 500 and 4500 to authorized peer IP addresses only.
- Credential Rotation: In the event that a management server is suspected to have been compromised, administrators should treat all administrative credentials and VPN pre-shared keys as potentially exposed and proceed with a full rotation.
Broader Implications for the Cybersecurity Landscape
The dual-front attack against both enterprise management systems and small-business gateways serves as a stark reminder of the evolving nature of supply chain and infrastructure-level threats. When the tools designed to protect the network become the vector of attack, the recovery process becomes significantly more complex.
The security industry has increasingly moved toward "Zero Trust" architectures, which assume that any device—even a security gateway—could be compromised. These events demonstrate that even in highly secure environments, the reliance on a single, monolithic security appliance can introduce systemic risk.
As the industry moves forward, it is expected that organizations will shift toward more granular monitoring of the management plane, treating it with the same level of scrutiny as the internal data center. For Check Point, the immediate focus remains on customer remediation and the forensic investigation of the July and September attacks. However, for the broader cybersecurity community, these incidents serve as a vital case study in the necessity of rapid patch deployment, the dangers of centralized administration, and the persistent threat posed by unauthenticated remote code execution flaws.
The current situation remains dynamic. Administrators are advised to monitor the official Check Point support portal continuously for updates, as the threat landscape surrounding these vulnerabilities is likely to change as attackers refine their methods in response to the patches being deployed globally.
Related posts: