Microsoft Issues Record-Breaking September Patch Tuesday Update Fixing 974 Vulnerabilities Amid AI Security Boom

Microsoft Corp. has unleashed its largest single security patch batch in history, releasing software updates designed to plug at least 974 security holes across its flagship Windows operating systems and auxiliary software ecosystem. This monumental September Patch Tuesday release obliterates the previous single-month record established just two months prior in July, when the technology giant issued fixes for at least 570 security flaws.
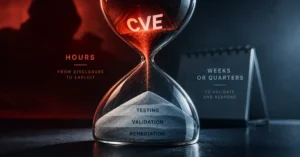
The staggering volume of September’s patches highlights a broader, industry-wide acceleration in vulnerability discovery. Driven increasingly by artificial intelligence and machine learning algorithms, software vendors are identifying and patching security gaps at a rate previously thought impossible. However, this exponential growth in automated vulnerability discovery has ignited a fierce debate among cybersecurity professionals. While AI is successfully unearthing massive quantities of code defects, enterprise security teams find themselves severely bottlenecked by the human-intensive requirements of testing, validating, and deploying such an overwhelming volume of updates without destabilizing corporate IT infrastructure.
The numbers defining the current threat landscape are unprecedented. With September’s deployment included, Microsoft’s cumulative total of patched vulnerabilities for the year has already surpassed 2,600. This figure is more than double the company’s previous historic record set in 2020, when 1,245 vulnerabilities were patched across the entire twelve-month calendar—a milestone crossed this year with a full quarter still remaining.
Active Exploits and Critical Vulnerabilities
Among the nearly one thousand vulnerabilities addressed in the September rollout, two stand out as "zero-day" flaws that are currently being actively exploited in the wild. Tracked as CVE-2026-81963 and CVE-2026-85880, both security holes allow malicious actors to elevate their privilege levels on targeted Windows systems, granting them deeper access and control than standard user accounts should legally possess. Cybersecurity agencies and threat intelligence analysts have urged immediate action on these specific identifiers, as active exploitation typically indicates that weaponized exploits are already circulating within criminal or state-sponsored hacker networks.
Furthermore, Microsoft classified 113 of the bugs addressed during this cycle as "critical." This severity rating denotes vulnerabilities that can be leveraged by automated malware or sophisticated attackers to seize total control over a vulnerable Windows machine, often requiring little to no interaction from the unsuspecting end-user.
Two critical vulnerabilities have drawn particular scrutiny from enterprise defenders. The first is CVE-2026-69730, a profound DNS weakness affecting Windows 10 and all iterations of Windows Server starting from Windows Server 2012 onward. Microsoft’s advisory warns that an unauthenticated attacker could exploit this vulnerability simply by transmitting a specially crafted network packet to an affected system. Given the foundational role of DNS in network architecture, the potential for widespread disruption is high, and security analysts view active exploitation as highly probable.
The second major threat is CVE-2026-69829, a remote code execution vulnerability residing within the Windows Shell. This flaw earned a near-maximum Common Vulnerability Scoring System (CVSS) base score of 9.8 out of 10. What makes this vulnerability especially perilous for system administrators is its combination of low attack complexity, zero required user interaction, and the absence of any prerequisite privileges on the host machine. An attacker can theoretically trigger the flaw remotely, bypassing perimeter defenses if systems are left unpatched.
The AI Factor: Larger Haystacks, Not More Needles
Microsoft’s record-breaking patch batch is not an isolated phenomenon. Across the technology sector, major software vendors—including Adobe, Cisco, Google, Mozilla, and Oracle—have reported a dramatic escalation in the volume and cadence of their security updates. Many of these organizations have openly credited AI-assisted research tools for accelerating their ability to scan massive codebases and identify latent vulnerabilities. The trend is moving so rapidly that Google announced plans to transition its own security updates to a bi-weekly release schedule to cope with the influx of findings.
The integration of artificial intelligence into vulnerability research has fundamentally altered the cybersecurity paradigm, though perhaps not entirely in the ways engineers initially anticipated. Satnam Narang, senior staff research engineer at Tenable, offered a nuanced perspective on the shifting metrics of software security.
"AI-assisted vulnerability discovery in 2026 is creating larger haystacks, but it isn’t finding more needles," Narang observed. He emphasized that while the raw count of documented vulnerabilities is skyrocketing, the actual subset of those flaws that pose an imminent, practical threat to the average organization remains relatively stable. "It’s critical that organizations understand which vulnerabilities actually apply to them, whether they pose a threat by being reachable and exploitable, and prioritize remediation based on this risk context."

This sentiment underscores a central frustration among enterprise defenders: the sheer administrative overhead required to parse, evaluate, and test hundreds of vendor advisories each month.
The Enterprise Burden: Testing, Deploying, and Burnout
For enterprise environments, Patch Tuesday is rarely a simple "click-and-install" affair. Tyler Reguly, associate director of security research and development at Fortra, highlighted the fundamental engineering hurdle that complicates rapid patching: the interdependence of modern software architectures.
"One core challenge with deploying Windows updates is that they need to be tested before being installed across an organization because not all third-party software works seamlessly in the face of changes to the underlying operating system," Reguly explained. An update designed to fix a deep kernel vulnerability can inadvertently break legacy enterprise resource planning (ERP) software, specialized accounting tools, or custom internal applications, forcing IT departments to walk a tightrope between security and operational continuity.
The relentless pace of record-shattering patch bundles is taking a tangible toll on the human capital responsible for maintaining corporate security. Reguly issued a stark warning to corporate leadership regarding the sustainability of current incident response and systems administration workloads.
"It’s time to put our CISOs and CSOs on notice," Reguly stated. "How are you helping your teams through these difficult times? Do you have your teams deploy after hours and on weekends to avoid disruption to the business environment? Do you reward them for that effort? Time to dig into your budget and buy dinner for your teams that are working on Saturday to get patches rolled out before users return to work on Monday."
Beyond financial compensation, industry analysts suggest that organizations must accelerate the adoption of automated patch management platforms, risk-based prioritization frameworks, and virtual patching solutions (such as web application firewalls and intrusion detection systems) to shield networks while thorough testing protocols are executed.
Guidance for Consumers and Enterprise Administrators
While enterprise information technology departments face complex testing matrices, the situation for individual, non-enterprise Windows users is comparatively straightforward, albeit increasingly urgent. Regular users do not need to conduct compatibility testing before applying updates, but they do bear the responsibility of ensuring their systems are not ignoring automated prompts.
With Microsoft’s patch releases expanding at an exponential rate, allowing updates to accumulate month after month creates a compounded security risk and increases the likelihood that a future update installation will encounter a system conflict. Cybersecurity experts strongly advise domestic users to enable automatic updates or manually check the Windows Update utility regularly.
For enterprise system administrators navigating the September 2026 update cycle, community-driven resources have become vital lifelines. Administrators are advised to monitor platforms such as AskWoody (askwoody.com) for real-time reports of installation anomalies, known bugs, or withdrawal notices regarding specific patches. Additionally, the SANS Internet Storm Center has published a comprehensive, per-patch breakdown categorized by severity and operational urgency to help security teams triage the nearly one thousand fixes.
As artificial intelligence continues to reshape both offensive security research and defensive engineering, the software industry appears to have crossed a threshold into an era of high-volume, continuous vulnerability remediation. How organizations adapt their human processes, budgets, and technological infrastructure to absorb this relentless deluge of updates will define the state of enterprise cybersecurity for the remainder of the decade.