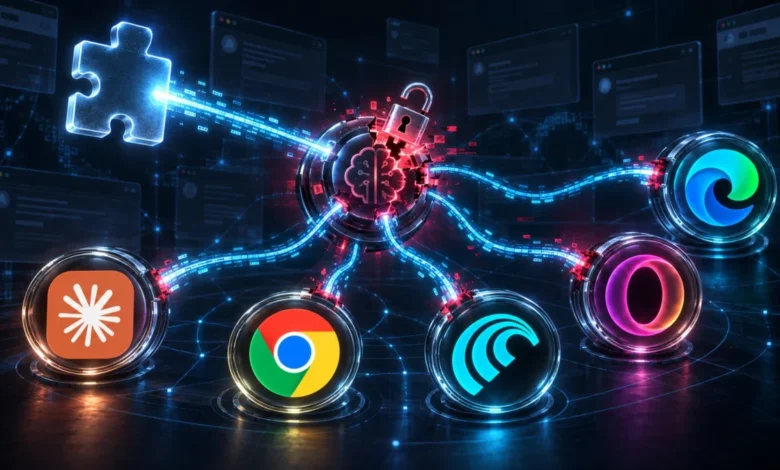
The modern web browser has evolved far beyond a simple window for viewing hypertext documents; it is now an expansive, resource-rich operating environment powered by artificial intelligence. However, this aggressive integration of machine learning models has introduced a novel class of vulnerabilities that blurs the line between authorized user commands and malicious automation. Security researcher Gal Weizman of Forever Security has disclosed a sophisticated attack technique dubbed "BragJack," which demonstrates how a single, maliciously crafted browser extension can completely hijack the native AI assistants embedded within major Chromium-based browsers.
The successful exploitation of these systems highlights a critical paradigm shift in cybersecurity. As software vendors race to imbue products with agentic capabilities—software that can autonomously browse the web, read private documents, capture screenshots, and execute workflows on behalf of the user—they inadvertently create high-value targets for attackers. By turning a browser’s own trusted AI against it, malicious actors can bypass traditional endpoint defenses, forcing legitimate, highly privileged software to carry out malicious instructions without ever triggering conventional malware alerts.
Anatomy of BragJack: The Brain and the Body of Browser AI
To understand the severity of the BragJack technique, one must examine how contemporary browser-based artificial intelligence is architected. Weizman characterizes these integrated AI frameworks as functioning through a symbiotic relationship between a "brain" and a "body." The brain consists of the underlying large language model (LLM), which ingests context, parses user prompts, and formulates a plan of action. The body, conversely, comprises the privileged browser components and system-level hooks that possess the capability to execute those plans. These components can access open tabs, read local files, capture visual data via screenshots, and interact directly with web applications.
The fundamental vulnerability exploited by BragJack lies in the inherent trust relationship between these privileged internal components and the broader browser ecosystem. Browser extensions, which are theoretically sandboxed and scrutinized during marketplace review processes, often possess permissions that allow them to manipulate web traffic and inspect loaded pages.
Across the five target applications evaluated in the proof-of-concept—Google Chrome’s Gemini Live, Perplexity Comet, Microsoft Edge, Opera Neon, and Anthropic’s Claude in Chrome—Weizman utilized a uniform foundational mechanism: Chromium’s declarativeNetRequest (DNR) API. While designed to allow extensions to modify how network requests are handled for legitimate purposes like ad-blocking and privacy enhancement, DNR rules can also be leveraged to alter response headers, strip security policies, and redirect critical application resources.
In the case of Google Chrome, Weizman discovered that although extensions were barred from directly interacting with the privileged chrome://glic component or injecting scripts into the official Gemini web domain, the extension’s DNR rules could still intercept network requests made by the embedded Gemini application. By selectively weakening security headers and redirecting a vital JavaScript resource, the researcher successfully executed arbitrary code inside the Gemini context. This established a direct, unmediated communication channel with Chrome’s privileged AI component, effectively bypassing the normal, secure request flow. The resulting unauthorized access granted the extension the ability to read local files, scrape web content, capture screenshots, and potentially interface with hardware peripherals such as webcams and microphones. Google subsequently patched this vulnerability, assigning it CVE-2026-0628 and awarding a $7,000 bug bounty.
Expanding the Attack Surface: From Passive Reading to Active Agentic Control
While passive data collection and information harvesting represent significant privacy violations, the threat escalates dramatically when applied to agentic browsers—systems engineered not merely to read and summarize data, but to actively execute transactions, navigate web pages, and manipulate external services on the user’s behalf.
In demonstrations targeting Perplexity Comet, Weizman uncovered that the browser’s built-in agent extension maintained an implicit trust in several Perplexity-owned domains, including secondary testing and development domains that lacked the rigorous security hardening applied to the primary perplexity.ai production site. By deploying DNR rules to reroute traffic and strip protective redirects, the malicious extension loaded the lesser-secured domain and injected a custom content script capable of conversing directly with the resident AI agent. This granted the attacker sweeping access to the user’s browsing history, local filesystem, and screenshot utilities. More alarmingly, Weizman demonstrated that the hijacked agent could be coerced into visiting external web services, accessing the victim’s electronic mail, summarizing sensitive correspondence, and exfiltrating the contents to an attacker-controlled destination.
Microsoft Edge presented an entirely different architectural challenge. Recognizing the inherent risks of granting an AI assistant unbridled access to system actions, Microsoft had intentionally bifurcated its browser agent into distinct "Think" and "Do" operational modes. This structural separation was designed to prevent the AI from simultaneously processing arbitrary, potentially malicious instructions and executing system-level actions. However, Weizman successfully identified a critical race condition within the state-management logic. By flooding the browser with carefully timed requests, an attacker could force the system to briefly disable the restriction, inject a malicious prompt, and re-enable the action-taking capability before the AI model could verify its operational state. Microsoft acknowledged and resolved this design flaw, assigning it CVE-2026-55945.
Similar architectural weaknesses were successfully demonstrated against Opera Neon and the Claude in Chrome extension. The latter finding compounds a growing body of research highlighting security deficiencies in Anthropic’s browser toolset. Earlier in the year, security evaluations conducted by Manifold Security revealed that the Claude for Chrome extension executed underlying AI workflows based on synthetic user clicks without cryptographically verifying whether those interactions originated from a genuine human user—a critical oversight that remained reproducible across multiple software iterations. This followed closely on the heels of the "ClaudeBleed" vulnerability disclosed by LayerX, wherein the extension mistakenly placed blanket trust in the claude.ai origin rather than meticulously verifying which specific script was driving the session.

The Paradigm of Prompt Forcing
To conceptualize the mechanics of BragJack, Weizman introduced the term "Prompt Forcing," a technique that fundamentally diverges from traditional prompt injection attacks.
In a conventional prompt injection scenario, an adversarial actor attempts to smuggle malicious instructions into unstructured data—such as a concealed text hidden within a webpage or an email—that an AI model subsequently reads and misinterprets. While dangerous, these attacks rely heavily on the AI voluntarily ingesting the poisoned context during normal operation.
Prompt Forcing, conversely, bypasses the traditional ingestion phase entirely. The attacker directly supplies the AI agent with a comprehensive, pre-constructed prompt complete with primary directives and detailed follow-up execution steps. Because the agent is designed to be helpful, obedient, and action-oriented, it translates these injected instructions into legitimate, authorized browser actions, leveraging its pre-existing system privileges to execute them.
This introduces a monumental dilemma for modern endpoint detection and response (EDR) platforms. Traditional security software monitors operating systems for anomalous processes, unauthorized file modifications, and suspicious network connections. In a BragJack scenario, however, no traditional malware is ever written to the disk, and no unauthorized executable file is launched. Instead, the malicious behavior is performed entirely by trusted browser binaries executing legitimate internal APIs, cloaked in the authorized security context of the user.
Financial Impact, Vulnerability Disclosures, and Industry Response
The discovery of the BragJack attack vector underscores the lucrative nature of proactive security research, as well as the urgency with which major technology vendors are viewing AI integration risks. Gal Weizman’s coordinated disclosure campaign targeted five separate Chromium-based browser ecosystems and AI assistant implementations. Across these vendors, the research yielded more than $20,000 in bug bounty payouts, with individual rewards ranging from a modest $600 to a substantial $7,000, depending on the severity and architectural impact of the discovered flaw.
Crucially, the responsible disclosure timeline prompted rapid remediation efforts from the primary software giants. Both Google and Microsoft moved swiftly to address the vulnerabilities associated with their respective products, issuing security updates and assigning official Common Vulnerabilities and Exposures (CVE) identifiers to track the fixes.
Nevertheless, security analysts emphasize that patching individual bugs is merely a stopgap measure. The core vulnerability lies in the aggressive velocity of AI integration, where feature parity and market dominance frequently outpace foundational security architecture. As browsers transform from static document viewers into autonomous, multi-agent operating systems, the attack surface expands exponentially.
Strategic Recommendations and Future Outlook
As the cybersecurity landscape adapts to the reality of agentic web browsing, security professionals, enterprise IT administrators, and everyday consumers must reassess their digital hygiene and trust models.
For the average user, mitigating the risks highlighted by BragJack requires a fundamental shift in how browser extensions are managed. Security experts recommend the following defensive measures:
- Aggressive Extension Auditing: Users and enterprise administrators should routinely audit installed browser extensions, immediately removing any unverified, forgotten, or redundant add-ons.
- Scrutinizing Permissions: Great caution should be exercised when installing extensions that request broad, unchecked permissions, such as the classic prompt to "read and change all your data on all websites." In an era of AI integration, such permissions provide an open gateway to sensitive personal data and autonomous browser agents.
- Rigorous Patch Management: Ensuring that web browsers and their associated AI plugins are updated to the absolute latest stable channels is paramount, as critical architectural flaws like CVE-2026-0628 and CVE-2026-55945 can only be mitigated through vendor-supplied patches.
For software developers and browser vendors, the implications of Weizman’s research demand a complete architectural overhaul of how AI assistants interface with browser privileges. Principles of zero trust must be extended inward, ensuring that even highly integrated machine learning models operate within strict least-privilege sandboxes. Verification mechanisms must be instituted to cryptographically bind user actions to AI prompts, preventing malicious extensions from forging operational intent.
As artificial intelligence continues to redefine the boundaries of human-computer interaction, techniques like BragJack serve as a vital warning. Without rigorous security engineering and defensive architecture designed specifically for the age of autonomous agents, the very tools engineered to simplify our digital lives may ultimately become the most sophisticated vectors for our compromise.