Dutch Authorities Arrest Convicted Cybercriminal Pepijn van der Stap Amid Escalating International ShinyHunters Attacks

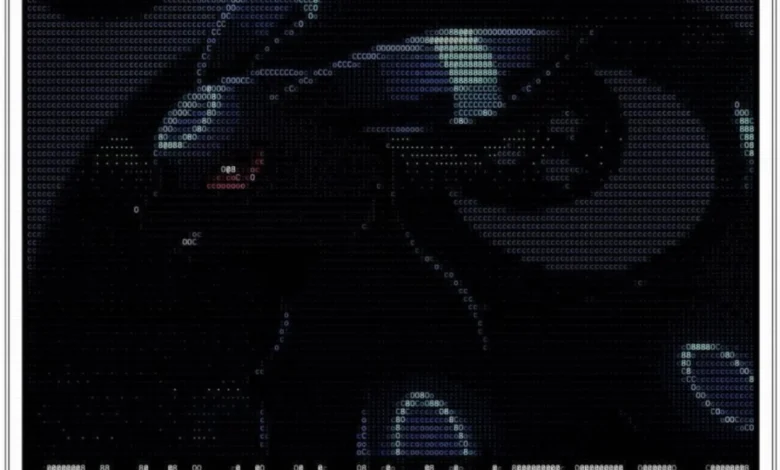
The global cybersecurity landscape experienced a violent tremor this month following the high-stakes arrest of 24-year-old Dutch cybercriminal Pepijn van der Stap by authorities in the Netherlands. Van der Stap, previously convicted in late 2023 for orchestrating extensive data thefts and extortion campaigns, was taken into custody on or around September 16, 2026. Law enforcement action against van der Stap immediately triggered a severe and unprecedented escalation by the prolific, internationally feared cybercrime syndicate known as ShinyHunters.
In the immediate wake of the detention, remaining members of the collective launched a brazen offensive across the globe. This retaliation included a deeply invasive cyberattack against the Federal Bureau of Investigation (FBI), a targeted extortion campaign against the prominent Russian-speaking ransomware group Cl0p, and a massive supply-chain data harvesting operation impacting major corporate and governmental infrastructure. The unfolding events highlight the volatile dynamics of modern cybercrime syndicates, internal turf wars, and the relentless cat-and-mouse game between elite threat actors and global law enforcement agencies.
The Double Life of Pepijn van der Stap
According to multiple sources familiar with the ongoing international investigation, the suspect detained in mid-September is indeed Pepijn van der Stap, a resident of Almere and Lelystad in the Netherlands. Van der Stap’s criminal history first captured global headlines during his 2023 trial, where prosecutors demonstrated that his data theft and corporate extortion schemes had generated illicit profits ranging between €1.5 million and €2.7 million.
During legal proceedings, van der Stap famously admitted to maintaining a Dr. Jekyll and Mr. Hyde lifestyle. By night, he operated under the well-known hacker alias “Umbreon,” infiltrating corporate networks, extorting vulnerable victims, and auctioning stolen databases on English-language cybercrime forums such as RaidForums and Breached. By day, however, van der Stap masqueraded as a legitimate software engineer. He maintained professional employment with Hadrian, an Amsterdam-based cybersecurity startup, and actively volunteered his technical expertise for the Dutch Institute for Vulnerability Disclosure (DIVD), a prominent nonprofit security research organization.
Van der Stap ultimately confessed to the string of cybercrimes and was sentenced to four years in prison, with one year suspended. Citing severe psychological challenges, including post-traumatic stress disorder stemming from childhood trauma, van der Stap elected to remain incarcerated rather than serving his sentence under house arrest, arguing he could receive better mental healthcare behind bars. He was subsequently released in December 2025.

In a September 9, 2026, interview with security journalists, van der Stap positioned himself as a reformed individual genuinely trying to rebuild his life and contribute positively to society. At the time of his second arrest, he was employed as an offensive security lead at Neo Security, a Dutch cybersecurity firm that has thus far declined to comment on the matter. Following the interview, van der Stap abruptly ceased all communication. Dutch police later confirmed the arrest of a 24-year-old man in connection with the broader ShinyHunters investigation, scheduling his formal appearance before the Rotterdam District Court. In a shocking late development, Dutch media outlet RTL reported that investigators are also examining whether van der Stap attempted to orchestrate at least two murders abroad.
A Timeline of Escalation and Retaliation
The timeline surrounding van der Stap’s arrest maps directly onto a dramatic spike in aggressive cyber operations conducted by the ShinyHunters collective.
In February 2026, Dutch police released a public audio recording requesting assistance in identifying a native Dutch speaker who successfully social-engineered their way into Odido, the Netherlands’ largest mobile telecommunications provider. Posing as an authorized individual, the attacker tricked an Odido employee into authenticating credentials on a spoofed phishing website, enabling the theft of sensitive data belonging to more than 6.2 million Dutch citizens. When local media reported on the audio leak, ShinyHunters aggressively confirmed the suspect’s affiliation with their group, releasing statements pledging full emotional, mental, and financial support—including retained criminal defense counsel—while hurling insults at Dutch law enforcement.
By mid-September 2026, following van der Stap’s detention, the syndicate pivoted away from targeted domestic intrusions toward high-profile international targets. On or around September 16, sources confirmed van der Stap’s arrest. Within days, ShinyHunters claimed responsibility for a disruptive compromise of apply.fbijobs.gov, the official job application portal for the FBI.
The Breach of the FBI and the Oracle PeopleSoft Vulnerability
The attack on the FBI recruitment portal exposed highly sensitive personally identifiable information (PII) belonging to more than 5,000 personnel. According to investigative reports by 404 Media and Reuters, the stolen data encompassed full Social Security numbers, job titles, and operational team rosters. These included records for special agents, threat intake examiners, and personnel assigned to major cybercrime units and foreign state-sponsored threat investigations. Furthermore, the exfiltrated files contained confidential medical and psychological evaluation records of FBI employees. The bureau formally confirmed the compromise via an official press release.

Security researchers from Mandiant and the Google Threat Intelligence Group (GTIG) revealed that ShinyHunters achieved access to the FBI infrastructure—alongside dozens of corporate and governmental systems across education, technology, healthcare, agriculture, and transportation sectors—by exploiting a critical zero-day vulnerability (CVE-2026-35273) in PeopleSoft, an enterprise human resources and payroll platform owned by Oracle.
Although Oracle rushed out a security patch to remediate the vulnerability, ShinyHunters utilized advanced URL-encoding evasion techniques to bypass web application firewall (WAF) mitigation rules issued by Mandiant. Throughout the defacement of the FBI job portal, the hackers left an unmistakable signature: an ASCII art rendering of the Pokémon character Umbreon, accompanied by a taunting message claiming credit for rooting systems since 2019. This visual Easter egg directly referenced van der Stap’s former hacker handle, fueling speculation about internal factions within the cybercriminal underworld.
Internal Turf Wars and the Rise of "Rey"
Intelligence analysts note that the recent campaign against the FBI and the Cl0p ransomware group represents a stark departure from ShinyHunters’ historical operational methodology. Industry experts attribute this strategic pivot to a leadership coup within the collective.
According to sources close to the investigation, the group experienced a hostile takeover led by a teenage cybercriminal from Amman, Jordan, known by the alias “Rey.” Rey operates as a core administrator within ScatteredLapsussHunters (SLSH), a hybrid cybercrime consortium combining elements of Scattered Spider, LAPSUS$, and ShinyHunters. First publicly unmasked by cybersecurity firm KELA in March 2025, Rey reportedly developed deep personal animosity toward van der Stap over operational control of the ShinyHunters brand and stolen data repositories. Investigators believe that incorporating the giant Umbreon imagery into the FBI portal defacement was a calculated maneuver by Rey to intentionally frame the imprisoned Dutch hacker.
The bad blood between SLSH and traditional ShinyHunters factions was further exacerbated by a chaotic partnership earlier in the year with TeamPCP, an upstart supply-chain hacking group. While TeamPCP successfully compromised global code repositories using malicious software, they struggled to monetize their stolen credentials. A brief alliance with ShinyHunters and SLSH quickly disintegrated after Mandiant—operating undercover within TeamPCP infrastructure—secretly leaked the stolen authentication keys to major cloud providers like Amazon and Microsoft, rendering them instantly invalid. The warring factions subsequently accused one another of betrayal, leading ShinyHunters to go rogue and independently execute high-yield corporate extortions. Security analysts estimate that ShinyHunters is on track to amass nearly $100 million in extortion payouts throughout 2026.
Global Law Enforcement Response and Strategic Implications

The international fallout from the ShinyHunters investigation underscores the escalating sophistication of transnational cyber syndicates and the increasing assertiveness of global law enforcement coalitions.
In response to the unprecedented string of attacks, Brett Leatherman, Assistant Director of the FBI’s Cyber Division, released a video statement commending Dutch law enforcement for their decisive action. Directing remarks at the remaining members of ShinyHunters, Leatherman issued a stern warning regarding the inevitability of identification and capture.
"Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left," Leatherman stated. "The longer you stay in this, the more we learn about you. You know how to find us, and we know how to find you. I suggest you reach out to us while the choice is still yours."
As Dutch authorities prepare to present Pepijn van der Stap before the Rotterdam District Court, cybersecurity analysts emphasize that the takedown of key infrastructure and high-level operatives disrupts criminal ecosystems temporarily, but often sparks volatile retaliatory cycles. The convergence of state-sponsored intelligence, private-sector threat hunting, and transnational police cooperation remains critical in dismantling the command structures of syndicates like ShinyHunters before they can execute further large-scale disruptions against global critical infrastructure.