Critical Security Flaw in Zimbra Collaboration Suite Exploited by Threat Actors for Data Exfiltration and Remote Access

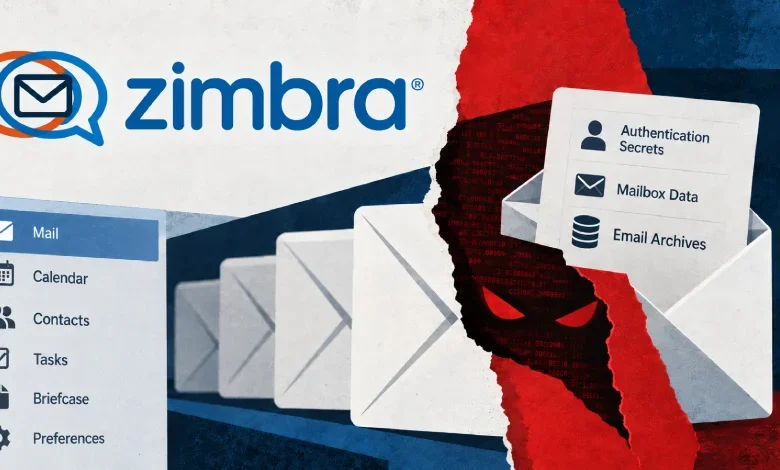
The cybersecurity landscape has faced a significant escalation in targeted attacks against enterprise communication infrastructure, following the discovery of an active exploitation campaign involving a high-severity vulnerability in the Zimbra Collaboration Suite (ZCS). Microsoft’s Security Research team recently disclosed that malicious actors have been weaponizing CVE-2026-73570, an unauthenticated command injection vulnerability, to gain full administrative control over internet-facing mail servers. This exploit allows adversaries to bypass authentication protocols, execute arbitrary code, and exfiltrate sensitive mailbox data, posing a severe risk to organizations that rely on Zimbra for internal and external communications.
Technical Analysis of CVE-2026-73570
The vulnerability, assigned a CVSS score of 8.9, stems from a flaw in the Simple Network Management Protocol (SNMP) notification feature within the Zimbra platform. Specifically, when the optional zimbra-snmp package is installed and SNMP notifications are enabled, the application fails to properly sanitize input. An attacker can trigger this vulnerability by sending a specially crafted Simple Mail Transfer Protocol (SMTP) request to an exposed server.
Because the attack vector does not require prior authentication or user interaction, it represents a "zero-click" exploit, making it highly effective against unpatched systems. Upon successful injection, the attacker can execute commands under the context of the "zimbra" service account. This level of access grants the threat actor the ability to manipulate system files, deploy persistent backdoors, and gain deep visibility into the organization’s email archives.

Chronology of the Exploitation Campaign
The timeline of this incident highlights a rapid transition from vulnerability disclosure to widespread exploitation. The security flaw was addressed by Zimbra on July 20, 2026, with the release of version 10.1.20. However, threat actors were quick to reverse-engineer the patch and identify the underlying flaw before the broader public was made aware of the risks.
- July 20, 2026: Zimbra releases patch version 10.1.20, resolving the command injection vulnerability.
- July 28 – August 7, 2026: Microsoft telemetry data identifies two distinct out-of-band scanning tools probing the injection path on various servers to validate command execution capabilities without delivering payloads.
- August 13, 2026: Formal public disclosure of the vulnerability occurs, confirming the risk to global users.
- Mid-August 2026: CERT Polska identifies active exploitation in the wild, providing early warnings and indicators of compromise (IOCs) for system administrators.
- Late August 2026: The U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds the flaw to its Known Exploited Vulnerabilities (KEV) catalog, issuing a mandatory directive for federal agencies to remediate the vulnerability by August 24, 2026.
Tactics, Techniques, and Procedures (TTPs)
Microsoft’s research indicates a sophisticated multi-stage attack chain. Once the initial command injection is achieved, the attackers prioritize the establishment of persistence. This is often accomplished by deploying JSP web shells across Jetty and mailboxd application paths. These shells provide the attackers with a redundant, browser-based interface to execute further commands.
To maintain long-term access, the adversaries have been observed employing various "living-off-the-land" techniques. These include the use of cron jobs, systemd services, and the memfd_create system call to execute code directly in memory, which helps them evade traditional disk-based file integrity monitoring. Furthermore, researchers noted that attackers temporarily adjusted directory permissions to deploy payloads, only to restore them immediately afterward, effectively hiding their tracks from basic security audits.
In several instances, the attackers utilized a custom Go-based binary, identified as "Zimdown2," which serves as an installer for a more comprehensive remote-access agent, "Zimclient2." This agent is designed to support WebSocket, TLS, and raw TCP transports, enabling the threat actor to pivot through the victim’s internal network, perform bidirectional file operations, and set up SOCKS5 proxies to obscure the source of their traffic.

Data Exfiltration and Impact
The primary objective of this campaign appears to be the mass collection of credentials and mailbox data. By extracting data from /opt/zimbra/conf/localconfig.xml, attackers gain the necessary credentials to access the Zimbra MySQL and LDAP instances. With this access, they can systematically export the contents of database tables containing email configurations, mail rules, and authentication secrets.
The exfiltration process is equally methodical. Harvested data is compressed into ZIP archives and staged locally before being moved off-site. Microsoft observed one case where an attacker utilized the legitimate AzCopy tool—a command-line utility used for moving data to and from Azure storage—to attempt to transfer archived mailbox backups to a remote Azure Blob storage container. While evidence suggests this specific exfiltration attempt may not have completed, the use of cloud-native tools indicates a high level of operational security and an intent to blend in with legitimate network traffic.
Implications for Enterprise Security
The exploitation of CVE-2026-73570 serves as a stark reminder of the risks associated with exposed, internet-facing mail servers. Because these servers are inherently designed to receive and process external requests, they remain a primary target for threat actors seeking to gain a foothold in corporate environments.
The widespread nature of these attacks, which spanned multiple industries and geographic regions, suggests that the attackers are either part of a large, well-resourced cybercriminal syndicate or a state-sponsored entity focused on espionage. The ability to pivot from a simple mail server compromise to internal network traversal poses an existential threat to organizational security, as it allows for the potential theft of intellectual property, sensitive communications, and further lateral movement to compromise domain controllers or cloud infrastructure.

Recommendations and Mitigation Strategies
Security experts emphasize that immediate patching is the only definitive way to close the vulnerability. Organizations that have not yet updated their Zimbra Collaboration Suite to version 10.1.20 or later must prioritize this action immediately.
For environments where immediate patching is operationally difficult, security teams should implement the following compensating controls:
- Decommission SNMP: If the
zimbra-snmppackage is not required, it should be uninstalled entirely. Disabling SNMP notifications through the Zimbra administration console is also a critical step in reducing the attack surface. - Network Segmentation: Restrict access to SNMP and SMTP ports to known, trusted IP addresses using firewall rules. This prevents external, unauthenticated entities from sending the malicious requests required to trigger the injection.
- Credential Rotation: If a server is suspected of having been compromised, all Zimbra service account passwords, LDAP secrets, and API keys must be rotated immediately.
- Forensic Auditing: Administrators should review
/var/log/zimbra.logfor any signs of unauthorized service restarts or unusual activity. Additionally, deep scans of temporary and web application directories are necessary to identify any dormant JSP web shells or malicious scripts that may have been planted during the period of vulnerability. - Monitoring for Unusual Tooling: Monitor for the execution of unauthorized binaries, particularly those originating from the
/tmpdirectory, and look for anomalous network traffic patterns, such as the use ofAzCopyor other cloud storage synchronization tools that deviate from standard administrative behavior.
The ongoing evolution of this campaign underscores the critical importance of a proactive vulnerability management program. As threat actors continue to weaponize vulnerabilities with increasing speed, the window between the disclosure of a flaw and its active exploitation continues to shrink. Organizations must ensure they have robust incident response plans in place to detect, isolate, and remediate such threats before they result in significant data loss or operational disruption. The complexity of the payloads deployed in this campaign highlights that the modern threat landscape requires more than just perimeter defense; it necessitates deep, persistent monitoring of internal server processes to detect the subtle footprints left by sophisticated adversaries.