Ukrainian Authorities and FBI Arrest Four Key Members of International Ransomware Ring Linked to $40.5 Million in Extortion

In a landmark international law enforcement operation, Ukrainian authorities—acting in close coordination with the United States Federal Bureau of Investigation (FBI)—have successfully arrested four suspected core members of a sophisticated international ransomware syndicate. The arrests are the culmination of a rigorous two-year cross-border investigation into a cybercrime enterprise believed to be responsible for extorting more than $40.5 million from at least 28 prominent corporate victims worldwide.
The sweeping crackdown highlights the growing operational nexus between transnational cybercriminal syndicates and modern artificial intelligence, as investigators revealed that the group utilized AI-generated voice messaging platforms to execute highly convincing social engineering attacks. As governments and private enterprises worldwide grapple with an escalating tide of financially motivated cyber threats, this multi-jurisdictional strike marks a critical milestone in disrupting the global ransomware economy.
Scope and Scale of the Criminal Enterprise
According to statements released by Ukraine’s National Police, the dismantled organization operated as part of a much broader cybercrime network comprising over 60 active members spread across at least eight distinct jurisdictions, including Ukraine, Russia, and Kazakhstan. Notably, the broader criminal ecosystem harbored former operatives from the notorious Conti ransomware gang—a syndicate that officially shuttered its centralized operations in May 2022 only to splinter into smaller, highly agile affiliate groups such as BlackSuit and Royal.
While Ukrainian law enforcement has not yet formally linked the four arrested suspects directly to legacy Conti operations, the structural similarities in their target acquisition, negotiation tactics, and monetization strategies underscore the professionalized nature of modern cybercrime syndicates. The group systematically targeted high-value commercial sectors, including oil and gas, pharmaceuticals, manufacturing, logistics, financial services, and critical infrastructure.
Unlike indiscriminate spray-and-pray malware campaigns, this syndicate practiced meticulous reconnaissance. Before launching any network intrusion, the attackers thoroughly researched their targets’ financial standing, corporate asset structures, employee hierarchies, and known IT vulnerabilities. This intelligence allowed them to calibrate their extortion demands precisely to what the target company could pay without facing catastrophic insolvency.
The Anatomy of an Attack: AI-Powered Social Engineering
One of the most striking revelations from the two-year investigation is the syndicate’s pioneering use of artificial intelligence to automate and enhance their initial access vectors. Rather than relying solely on traditional phishing emails or brute-force credential stuffing, the perpetrators developed a proprietary platform capable of generating hyper-realistic AI voice messages.
Posing as internal IT support personnel, the attackers executed fraudulent telephone campaigns targeting corporate employees. Armed with synthesized voice data that mimicked authentic corporate helpdesk personnel, the fraudsters manipulated workers into divulging sensitive login credentials or installing rogue remote-access software such as AnyDesk or TeamViewer.
In forensic case studies detailed in Ukrainian court records, the human element of these intrusions is laid bare. During an attack on the Warren Oil Company in August 2024, fraudsters kept an employee engaged on an AI-assisted phone call while simultaneously navigating a corporate phishing portal. By manipulating the employee into handing over multi-factor authentication (MFA) codes, the actors secured a persistent foothold inside the corporate network.
Once inside, the actors moved laterally to harvest approximately 1.4 terabytes of sensitive corporate data. They subsequently deployed specialized encryptors—identified in court documentation as the Chaos ransomware—to lock down critical operational databases. The syndicate then leveraged a two-pronged extortion model: threatening to permanently withhold decryption keys while simultaneously promising to leak proprietary corporate data onto public dark-web leak sites unless a multi-million-dollar cryptocurrency ransom was paid.
Chronology of Major Incidents and Extortion Demands
The paper trail uncovered by Ukrainian investigators and corroborated by international cybersecurity researchers highlights a systematic pattern of multi-million-dollar corporate shakedowns spanning several years.
- May 2022: The Conti ransomware gang officially dissolves its public-facing brand, leading to the dispersal of its core operators into fragmented ransomware-as-a-service (RaaS) models and independent affiliate cells, which later birthed iterations like Quantum, Royal, and BlackSuit.
- August 2024: The syndicate breaches the Warren Oil Company, exfiltrating 1.4 terabytes of internal data. Following intense negotiations, the company ultimately transfers 84.5 Bitcoin—valued at approximately $5 million at the time—to restore operational capabilities.
- November 2024: Security researchers from French cybersecurity outlet LeMagIT and independent threat analysts track related ransomware strains targeting major industrial players, including Maxxis International-USA, with links pointing back to infrastructure utilized by the broader network.
- December 2024: Infrastructure and logistics-associated firm Newpark Resources falls victim to the syndicate, resulting in a targeted $1.5 million ransom payout.
- June 2026: Healthcare and corporate services provider Quantum Health is struck after an initial extortion demand of $15 million is negotiated down to a $5 million cryptocurrency settlement following the theft of over 1.5 terabytes of sensitive data.
Law Enforcement Action and Seizures
The coordinated takedown culminated in a massive domestic sweep across Ukraine. Acting National Police chief Maksym Tsutskiridze detailed that authorities executed 66 simultaneous search warrants spanning Kyiv and 11 distinct Ukrainian regions.
The raids resulted in the apprehension of four primary suspects, who have been formally notified of criminal charges related to participation in a criminal organization and unauthorized interference with automated electronic information systems. Under Ukrainian penal law, the accused face up to 15 years of imprisonment if convicted.
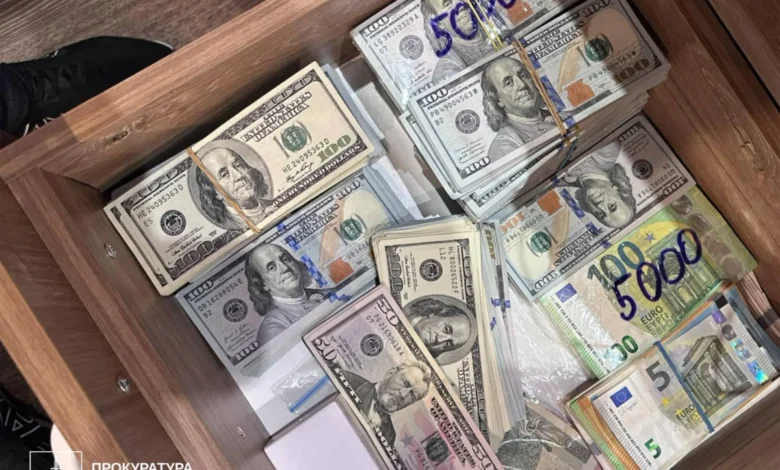
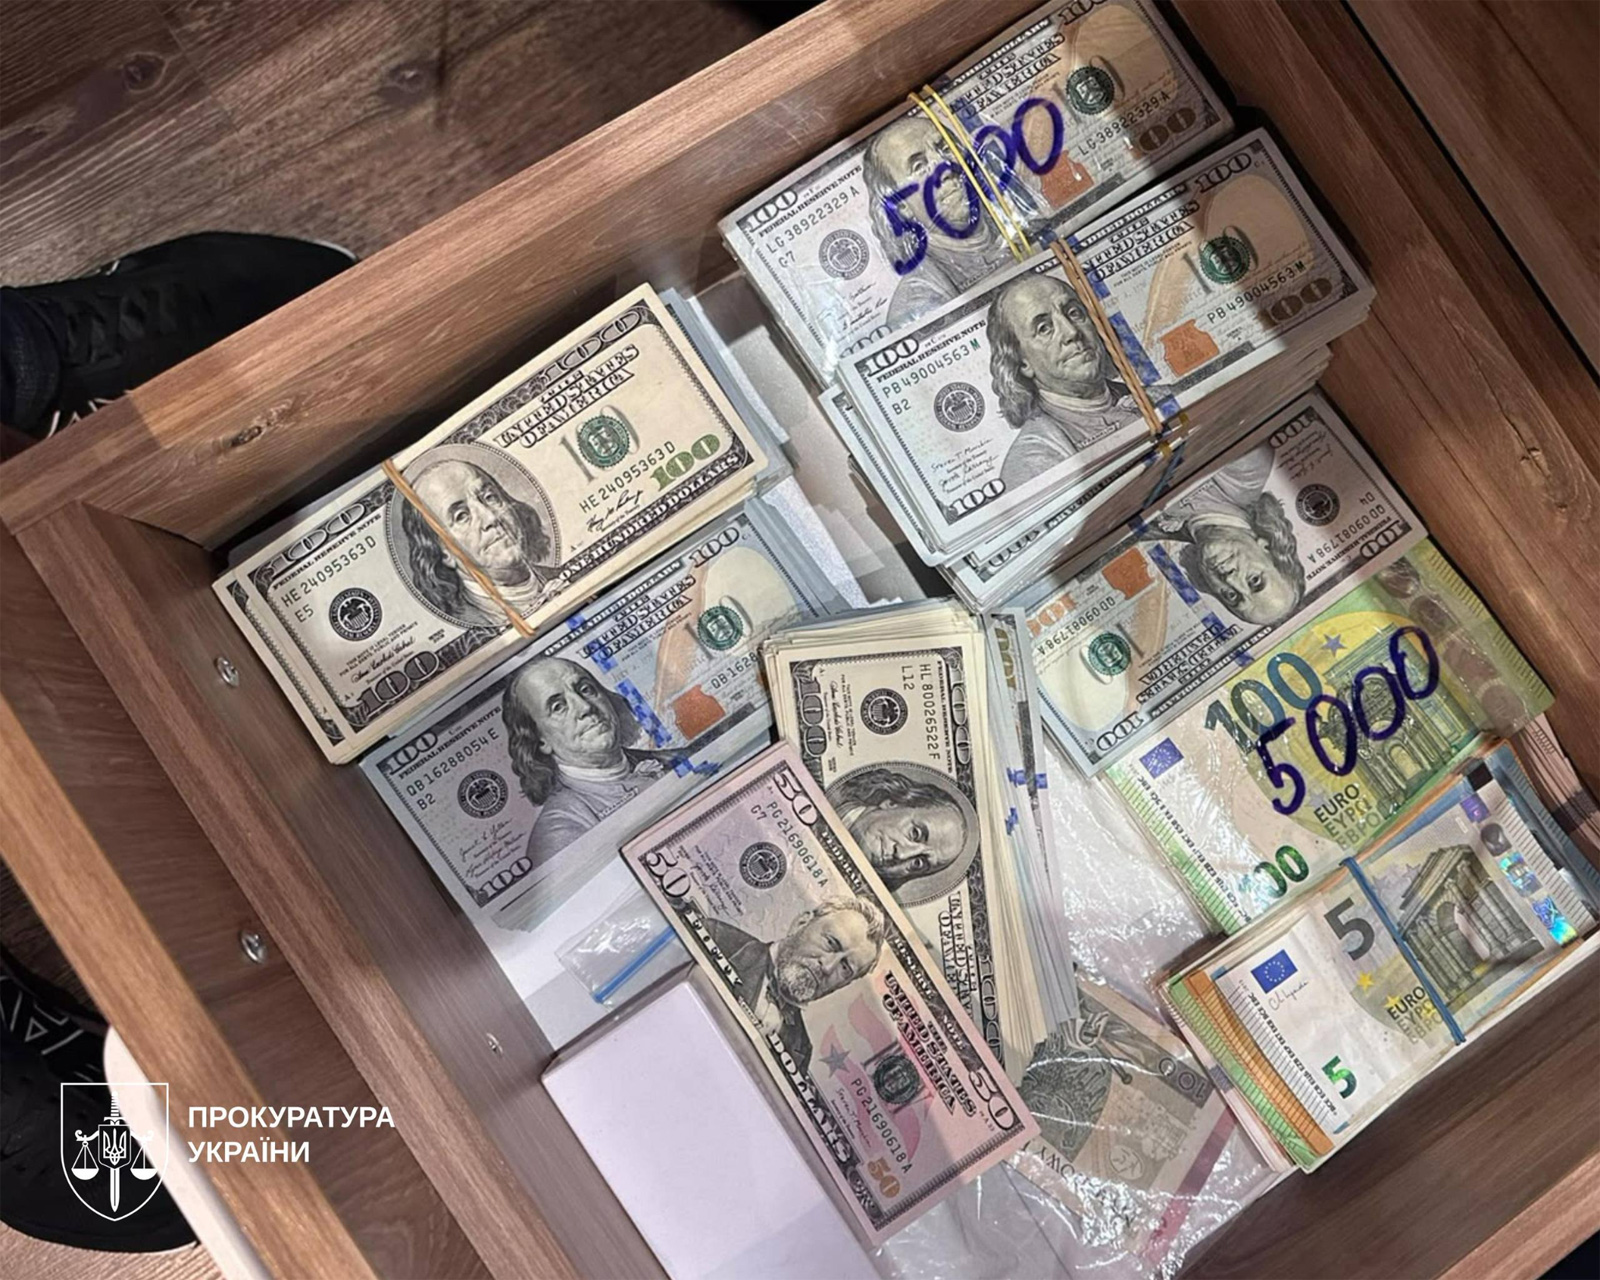
During the execution of the search warrants, law enforcement officials seized a trove of digital and physical evidence, including high-performance computing hardware, mobile devices, numerous bank cards, and substantial liquid assets comprising nearly $370,000 in U.S. currency alongside €20,000 in cash. The National Police subsequently released multimedia documentation of the raids, including suspect interrogations and intercepted audio recordings of ransom negotiations where operators demanded sums as high as $15 million.
Broader Implications for Global Cybersecurity
The successful arrest of these four individuals provides a vital case study in the efficacy of cross-border law enforcement cooperation. In recent years, cybercriminal syndicates have frequently operated with relative impunity from jurisdictions lacking robust extradition treaties or political alignment with Western law enforcement agencies. The active participation of Ukrainian authorities—operating under wartime conditions—alongside the FBI demonstrates that targeted intelligence sharing and joint operational planning can breach the protective bubble traditionally enjoyed by transnational cybercriminals.
However, security analysts emphasize that while apprehending four key members is a significant victory, it represents only a fraction of the broader operational ecosystem. The fluidity with which former Conti members and affiliated cybercriminals rebrand, deploy new ransomware variants (such as shifting from Chaos to BlackSuit-adjacent frameworks), and adopt emerging technologies like generative AI suggests that the ransomware threat vector will continue to evolve.
For corporate entities, the investigation reinforces the critical necessity of zero-trust architecture, advanced endpoint detection and response (EDR) solutions, and rigorous employee training regarding out-of-band identity verification for IT support requests. As criminal groups increasingly weaponize artificial intelligence to mimic trusted corporate communication channels, traditional perimeter defenses must be reinforced with robust behavioral analytics and strict multi-factor authentication protocols that cannot be easily bypassed through social engineering alone.
Related posts: